Zoho Creator REST API Integration
Most content about the Zoho Creator API stops at a sample request with a hardcoded token. That gets a developer through the first afternoon and nothing after it. The parts that actually determine whether an integration survives are the ones rarely written about: how OAuth refresh behaves in a long-running service, where the API limits sit and what happens when you reach them, why bulk operations exist and when to use them over record-by-record calls, and how to handle partial failure in a batch. This page covers those.
Home / Zoho Creator REST API Integration
What Separates a Working Integration From a Durable One?
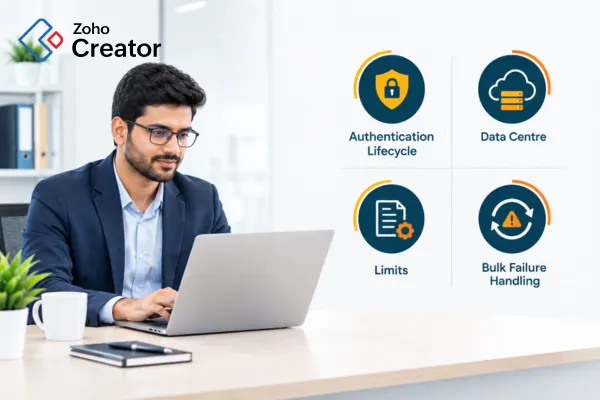
An integration that works on the developerβs machine and fails in month three usually fails for one of four reasons, none of which is the request syntax. The first is authentication lifecycle. Creatorβs API uses OAuth 2.0, and the access token is short-lived while the refresh token is the durable credential β so an integration that acquires a token manually and stores it will stop the first time that token expires, and one that requests a new refresh token on every run will hit the limit on concurrent refresh tokens. The second is data centre. Zoho operates separate data centres, and the API domain, accounts domain, and token endpoint all differ between them; a token issued in one will not authenticate against another, which is the cause of a large share of βinvalid tokenβ reports.
The third is limits. Creator enforces both API call limits by plan tier and record limits per request, and an integration written against a small dataset will silently process only the first page once volume grows. The fourth is failure handling in bulk. A bulk operation that partially succeeds returns a mixed result, and an integration that treats the response as a single success or failure will either reprocess records already written or lose the ones that failed. Getting these four right is most of what durability means.
Business Challenges We Solve
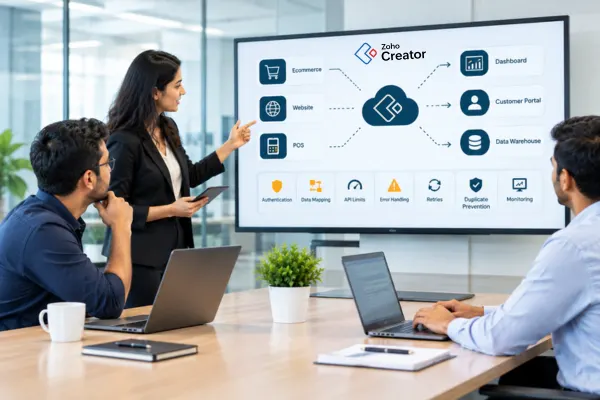
The integration requirements we are asked to build fall into recognisable shapes. An external system needs to push records into Creator β orders from an ecommerce platform, leads from a website, transactions from a POS. A Creator application needs to expose data outward β a dashboard in another system, a customer-facing status lookup, a feed to a data warehouse. A scheduled reconciliation needs to compare Creator against another system and correct differences. A bulk load needs to import a large dataset without hitting limits or leaving the target in a half-written state. Or a mobile or web front end built outside Creator needs to read and write Creator data directly.
Each pattern brings its own considerations around authentication, data mapping, API limits, error handling, retries, duplicate prevention, and monitoring. The integration needs to remain reliable when records fail, connections are interrupted, or data changes on either side. Designing these details upfront prevents an integration that works in testing from becoming a source of silent data loss or manual correction once it is running in production.
Whatβs Included?
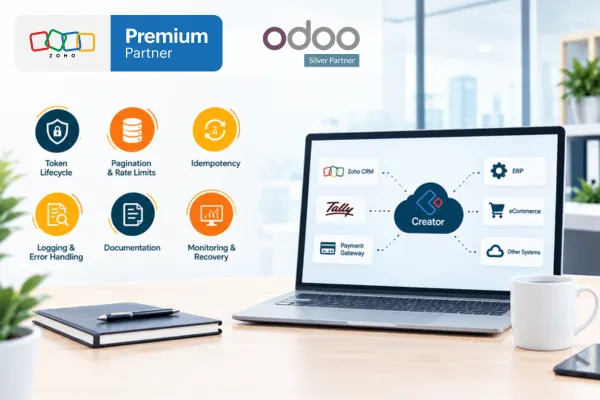
Each requires different handling, and the mistakes cluster. Integrations built record-by-record where bulk operations exist run slowly and consume call allowance unnecessarily. Integrations without pagination process the first page and silently ignore the rest. Integrations that do not handle the rate limit response treat it as a generic failure and either drop the record or retry immediately, making the situation worse. Integrations that store an access token rather than the refresh token break on expiry. And integrations without idempotency create duplicates every time a network timeout causes a retry of a request that actually succeeded. We build against these patterns explicitly, because each of them produces a failure that is invisible until data is already wrong.
OAuth Setup and Token Lifecycle Management
Client registration with correctly scoped permissions, refresh token acquisition, and an access token refresh cycle handled in code β with the refresh token stored securely and never regenerated per run.
Data Centre and Endpoint Configuration
The correct API, accounts, and token domains for your Zoho data centre configured explicitly rather than assumed, since a mismatch produces authentication failures that look like credential problems.
Scope Configuration to Least Privilege
API scopes limited to the specific operations and forms the integration requires, so a compromised credential cannot read or write beyond its purpose.
Pagination and Record Limit Handling
Record retrieval implemented with correct pagination so the integration continues to process complete result sets as data volume grows past the per-request limit.
Bulk Create, Update, and Import Operations
Bulk endpoints used where they exist rather than looping single-record calls, with batch sizing chosen against the limits and partial-success responses parsed record by record.
Rate Limit Detection and Backoff
The rate limit response detected specifically and handled with exponential backoff and a retry queue, rather than being treated as a generic error that drops or immediately retries the record.
Idempotency and Duplicate Prevention
Every write carrying a unique external reference checked before creation, so a retry following a timeout updates the existing record rather than creating a second one.
Error Logging, Alerting, and Reconciliation
Every failure logged with the request, the response, and enough context to diagnose it; alerting on failure classes that need attention; and a reconciliation view comparing record counts and key values between systems.
Zoho Applications We Use for This
Creator is the API target on every one of these; the rest appear when the integration spans more than one Zoho application.
Zoho Creator
The API target: form records, reports, file upload and download, and bulk operations, plus outbound invokeurl calls from Deluge
Zoho CRM
Where the integration spans both platforms and a consistent record identity must be maintained across them
Zoho Books
Financial record integration, where idempotency matters most because duplicate transactions carry real cost
Zoho Inventory
Stock and order integration where quantity errors from a mishandled partial failure have physical consequences
Zoho Flow
Used where a supported connector covers the requirement, avoiding custom API code that would then need maintaining
Zoho Analytics
Where the integrationβs purpose is feeding a reporting layer rather than transactional exchange
Where This Applies?
This applies wherever a Creator application must exchange data with something outside the Zoho ecosystem. Ecommerce platforms pushing orders into an operational application. POS and retail systems sending transactions. Warehouse and logistics providers exchanging dispatch and delivery data. ERP platforms where Creator holds a process the ERP does not. Banking and payment systems. Data warehouses and BI platforms pulling Creator data for consolidated reporting. Custom web or mobile front ends built outside Creator that read and write its data.
It applies with particular force to integrations that run unattended on a schedule. An interactive integration fails in front of a user who reports it; a nightly job fails silently and is discovered weeks later as missing data. Logging, alerting, and reconciliation reporting matter disproportionately in that context.
It also applies to businesses inheriting an integration built by someone else. These are frequently the ones carrying the four failure patterns above, and a review that tests token lifecycle, pagination, limit handling, and idempotency typically finds at least two of them present.
Ready to Build It Properly?
Why Choose Techvaria for API Work?
Techvaria is a Zoho Premium Partner whose teams build and maintain Creator integrations daily across India and the UAE. We write with token lifecycle, pagination, rate limit backoff, idempotency, and failure logging as standard rather than as hardening added later, because every one of those is invisible in testing and expensive in production. We document the integration β endpoints, scopes, field mapping, failure handling β so it remains maintainable, and Premium Partner status gives us escalation into Zoho engineering when behaviour turns out to be a platform characteristic rather than a code error.
We also design integrations with monitoring and recovery in mind, so failures can be identified and addressed without requiring constant manual intervention. Whether the requirement involves a single external application or several connected systems, the objective is to keep data moving reliably while preserving the integrity of the Creator application and the systems around it.
Hear From Our Clients
Industries We Serve
Frequently Asked Questions
OAuth 2.0. You register a client in the Zoho API console, request authorisation with the scopes your integration needs, and receive a refresh token. The refresh token is the durable credential and is used to obtain short-lived access tokens for actual API calls. The most common implementation error is storing an access token as though it were permanent, which breaks at the first expiry.
Most often a data centre mismatch. Zoho operates separate data centres, and the accounts domain, token endpoint, and API domain differ between them. A token issued against one data centre will not authenticate against another. The second common cause is insufficient scope β a token valid for reading but used for a write returns an authorisation failure that reads like an invalid credential.
Creator enforces call limits that vary by plan tier, and per-request record limits on retrieval and bulk operations. Both change periodically, so the current figures should be checked against Zohoβs documentation rather than assumed from an older integration. What matters architecturally is that limits exist: the integration needs pagination for reads and rate limit handling for writes regardless of what the current numbers are.
Whenever you are writing more than a handful of records. Bulk endpoints are faster and consume far less of your call allowance than an equivalent loop. The trade-off is that the response reports per-record outcomes, so the integration must parse it record by record rather than treating the call as a single success β which is where partial failures get lost in naive implementations.
Parse the response per record, mark the successful ones as processed with their returned IDs, and queue the failed ones with their specific error for retry or review. Treating the batch as atomic when the API does not is what causes either duplicate reprocessing or silently dropped records, depending on which way the assumption falls.
An idempotency key β a unique external reference stored on both sides β checked before every create. If the reference already exists, the operation updates rather than creates. This matters because a network timeout gives no indication whether the request succeeded, so retries are unavoidable and duplicates are the default outcome without the check.
Yes, through the invokeurl task in Deluge, which makes authenticated HTTP requests with configurable method, headers, and body. Creator can also receive inbound data via webhook. Most integrations we build use both directions, and the same disciplines β response validation, retry, logging, idempotency β apply to outbound calls as to inbound ones.
Yes, and it is a common request. The review tests token lifecycle and refresh behaviour, pagination at realistic volume, rate limit handling, idempotency, scope minimisation, and whether failures are visible. The output is a findings list with severity and a remediation plan. Most inherited integrations carry at least two of the four common patterns.